
Surviving the Blackout: How Sudanese Activists Outsmarted a Nation-State
Defensive Technology Use by Political Activists During the Sudanese Revolution
2021-05-01
Summary
Problem
Method
Results
Takeaways
Abstract
This research provides a sociotechnical analysis of defensive technology use by 13 political activists during the 2018-2019 Sudanese revolution. It uncovers how activists navigated state-sponsored censorship and internet blackouts using a suite of "low-tech" but effective adaptations in communication and device security.
## TL;DR
In a world where state-sponsored surveillance and internet shutdowns are becoming preferred tools of repression, how do activists survive? This paper explores the **Sudanese Revolution (2018-2019)** through the eyes of 13 front-line activists. It reveals a fascinating paradox: while high-tech encryption is vital, "low-tech" ingenuity—manually deleting messages, using coded SMS, and leveraging international relatives for 2FA—was the real hero of the movement.
## The High-Stakes Threat Landscape
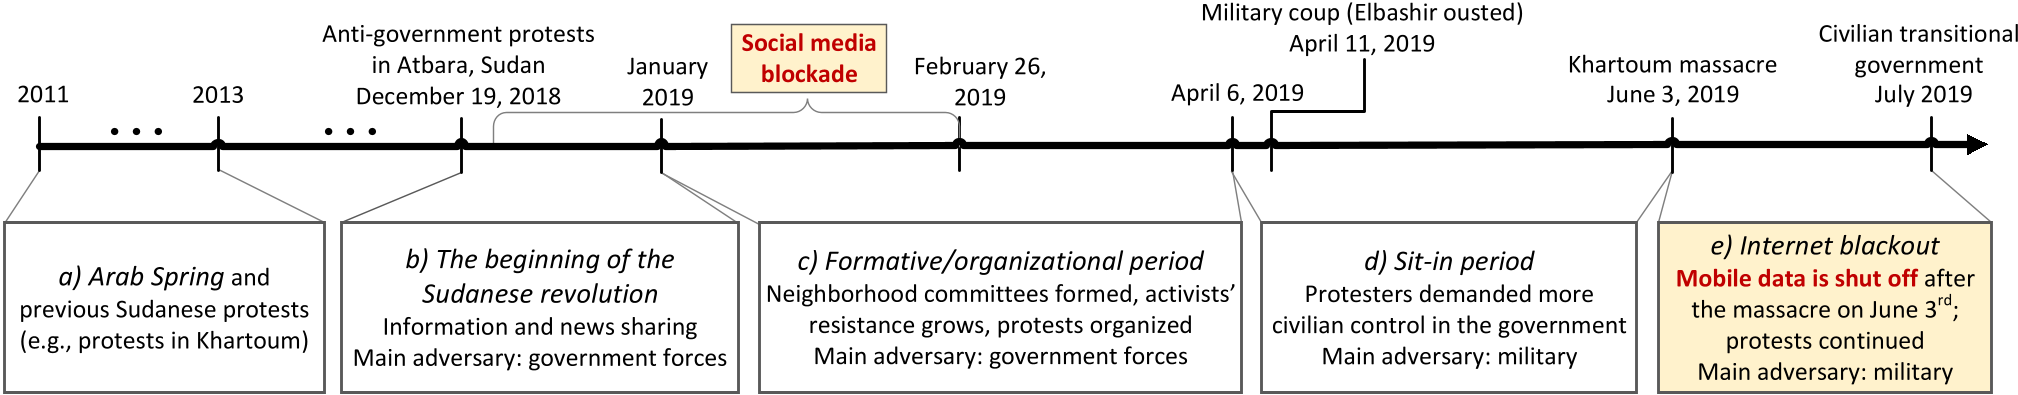
During a revolution, technology isn't just a tool; it's a liability. The Sudanese government, through the National Intelligence and Security Services (NISS), didn't just monitor the web—they owned it. The threat model wasn't hypothetical:
* **Total Blackouts**: A 5-week mobile data shutdown following the Khartoum massacre.
* **Physical Seizure**: Authorities would arrest protesters and demand phone passcodes on the spot.
* **Infrastructure Control**: Sanctions meant Google Play and the App Store were blocked, forcing users into insecure third-party download methods.
## Methodology: Digging into Subversive Tech
The researchers used semi-structured interviews and a rigorous qualitative coding process (reaching 98.7% intercoder agreement) to map how activists adapted.
## The Core Struggle: Trust vs. Infrastructure
### 1. The 2FA Trap
Because of US sanctions, Sudanese phone numbers were often rejected by platforms like Twitter for Two-Factor Authentication (2FA). Activists bypassed this by "outsourcing" their security: they used the phone numbers of relatives in the diaspora (USA, Qatar, Egypt) to receive verification codes.
### 2. Low-Tech Concealment
Rather than relying on complex encryption that might signal "guilt" to an officer, activists used existing UI features for subversive ends:
* **iOS ScreenTime**: Used to hide social media apps during protests.
* **Android TwinApps**: Creating a "clean" second instance of a pro-government social profile.
* **Manual Sanitization**: Most activists would completely wipe their WhatsApp history before attending a march, choosing data loss over arrest.
### 3. Fighting the Blackout
When the internet died, the movement didn't. Activists reverted to "analog" digital use:
* **Coded SMS**: Using innocuous language over unencrypted cellular networks.
* **Phone Trees**: Manually relaying news from the few landline connections still active.
* **Mesh Failures**: Interestingly, apps like *FireChat* failed due to a lack of "critical mass" and the difficulty of downloading an app once the internet was already gone.
## Design Principles for the Future
The paper concludes that security tools are often built with "WEIRD" (Western, Educated, Industrialized, Rich, Democratic) assumptions. To support activists, developers should consider:
* **Sanitization on Trigger**: A "panic button" that wipes specific data or triggers a decoy OS.
* **Mainstream Mesh**: Mesh networking shouldn't be a separate app; it should be a "fallback mode" within WhatsApp or Telegram.
* **Alternative Authentication**: Platforms must stop relying on local SIM cards for 2FA in sanctioned or high-risk regions.
## Conclusion: The Resilience of the "1000 Person"
In Sudan, a tight-knit core of roughly 1,000 activists (the "1000 person" joke) created a human firewall. Their success proves that while tech can be blocked, social trust is much harder to censor.
**Critical Analysis**: The primary limitation here is the small sample size (13 participants) and the focus on Khartoum. However, the depth of the "field-tested" insights provides a roadmap for what "Resilient Design" actually looks like in a collision with a nation-state.