
COMPA: Shielding the Social Fabric from Account Hijacking
Towards Detecting Compromised Accounts on Social Networks
This paper presents COMPA, the first automated system designed to detect compromised social network accounts by modeling individual behavioral profiles. It successfully identifies both high-profile account hijacks and large-scale malicious campaigns on Twitter and Facebook.
TL;DR
As cybercriminals shift from creating fake bots to hijacking legitimate, high-trust accounts, social media platforms face a crisis of authenticity. COMPA is the first system that creates a digital "behavioral fingerprint" for every user—monitoring habits like what apps they use, when they post, and who they talk to. It doesn't just catch mass spam; it can detect a single malicious tweet from a high-profile account like the Associated Press or Skype before it causes market chaos.
The Motivation: When Trust Becomes a Weapon
Most social media security handles "fake accounts" (Sybils) well. However, if a trusted news agency's account is compromised, the damage is immediate. In 2013, a single fake tweet about a White House explosion wiped out $136 Billion in market value in seconds.
Existing defenses fail here because:
- The account is "real": It has years of legitimate history.
- Minimal footprint: A compromise might involve only one or two messages, making it invisible to "spam campaign" detectors.
- Manual delay: Detection currently relies on humans noticing the error, which often takes hours—long after the viral damage is done.
Methodology: The Behavioral Fingerprint
COMPA operates on a simple but powerful intuition: Users are creatures of habit. If you always post from an iPhone at lunch in English, and suddenly "you" post from a web portal at 3 AM in Russian with a link to a pharmacy site, something is wrong.
1. The 7 Dimensions of Behavior
COMPA models user activity across seven distinct statistical features:
- Time: Identifying the "quiet periods" and active hours.
- Source: Training on the specific OAUTH applications used (e.g., TweetDeck vs. Web).
- Language & Topic: Monitoring shifts in linguistics and hashtag usage.
- Links & Interactions: Tracking the domains usually shared and the "inner circle" of users interacted with.
- Proximity: (For Facebook) Checking if interactions suddenly jump to a new geographic network.
2. The Architecture: Anomaly Detection vs. Grouping
For high-profile accounts, behavior is so consistent that a single deviation is often enough to trigger an alert. For regular users, who vary more, COMPA adds a Group Similarity layer.
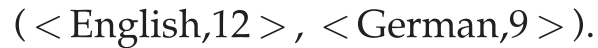
The logic follows a weighted sum of feature anomalies. If a message is locally anomalous AND belongs to a cluster of similar messages across other accounts, it is flagged as a "Campaign."
Experimental Breakthroughs
The researchers tested COMPA against a staggering 1.4 Billion Twitter messages and 106 Million Facebook posts.
Performance on High-Profile Breaches
COMPA successfully "back-detected" major historical hacks:
- Associated Press: Detected because the hacker used the Twitter website instead of the agency's standard
SocialFlowapp, and omitted their habitual links. - Skype: Flagged the anti-Microsoft messages that took the official team over two hours to notice.
- The Chipotle "Fake" Hack: In a brilliant "Turing Test" for the system, Chipotle faked a hack for publicity. COMPA did not flag it, correctly identifying that the messages still came from their usual apps and editors—proving the system isn't easily fooled by content shifts if the metadata remains consistent.
Large Scale Detection Statistics
| Metric | Twitter (Text Similarity) | |
|---|---|---|
| Identified Compromises | 9,362 Groups | 671 Groups |
| Total Accounts Saved | 343,229 | 11,499 |
| False Positive Rate | ~3.6% | ~3.6% |
Critical Insight: Why This Changes the Game
The real value of COMPA lies in its Inductive Bias. Instead of trying to define what "malice" looks like (which is a moving target), it defines what "you" look like.
Limitations & Future Work: While COMPA is robust, it faces challenges with multi-actor accounts (like The Guardian, where dozens of journalists post using different styles), which can lead to high false positives. Additionally, sophisticated attackers might attempt "mimicry attacks"—slowly poisoning a behavioral profile over time to make malicious activity look "normal."
Conclusion
COMPA proves that our digital habits are as unique as our physical signatures. By shifting the defensive focus from the content of the message to the context of the user, social networks can finally protect the trust they've spent years building.