
Hitchbot: The Evolution of SNS Malware Through Social Hitch-hiking
Hitchbot - Delivering Malicious URLs via Social Hitch-Hiking
This paper introduces Hitchbot, a stealthy malware framework that spreads malicious URLs via "social hitch-hiking." Instead of mimicking human behavior, it intercepts and replaces legitimate links sent during real conversations on SNS or IM platforms with homographic or malicious variants, achieving a near 100% click-through rate in concept tests.
TL;DR
Hitchbot is a sophisticated attack framework that turns legitimate users into unwitting spreaders of malware. By intercepting the OS input chain, it replaces safe URLs with malicious ones during real-time conversations. Because the link appears in a trusted context, it effectively bypasses traditional bot-detection systems and achieves a near-perfect infection rate.
Background: The Trust Deficit of Traditional Bots
In the early days of Social Networking Service (SNS) attacks, malware used a "spray and pray" approach—compromising an account and blasting generic links to everyone in the contact list. However, modern security headers and behavioral analytics have made this difficult. To succeed, a bot must mimic human-style interaction, a task that remains high-effort and low-reward.
The researchers from The Chinese University of Hong Kong propose a paradigm shift: Don't simulate the human; exploit the human's existing conversation.
Problem & Motivation: The Weak Link in the I/O Chain
Existing defenses focus on what is being sent (content filtering) or how much is being sent (rate limiting). However, they ignore the integrity of the data between the user's fingertips and the network card. The authors identify that human users provide the perfect "camouflage" for malicious links. If a user naturally shares a link with a friend, that friend is highly likely to click it. By "hitch-hiking" on this event, the malware inherits the user's social capital and trust.
Methodology: Four Paths to Interception
The core of Hitchbot lies in its ability to manipulate the Interactive User Input/Output Chain. The authors identify four distinct Attack Vectors (AV) along this data flow:
- AV I: HTML Form Replacement: Injecting JavaScript into browsers to modify
<input>fields before form submission. - AV II: Keystroke Hooking: Using Win32 Hooks to intercept keyboard messages in the OS queue and replacing URL characters in real-time.
- AV III: Clipboard Hijacking: Monitoring the
WM_DRAWCLIPBOARDmessage to swap links the moment a user copies a URL. - AV IV: Packet Modification: Using tools like Snort-inline to replace plaintext URL payloads in network packets.
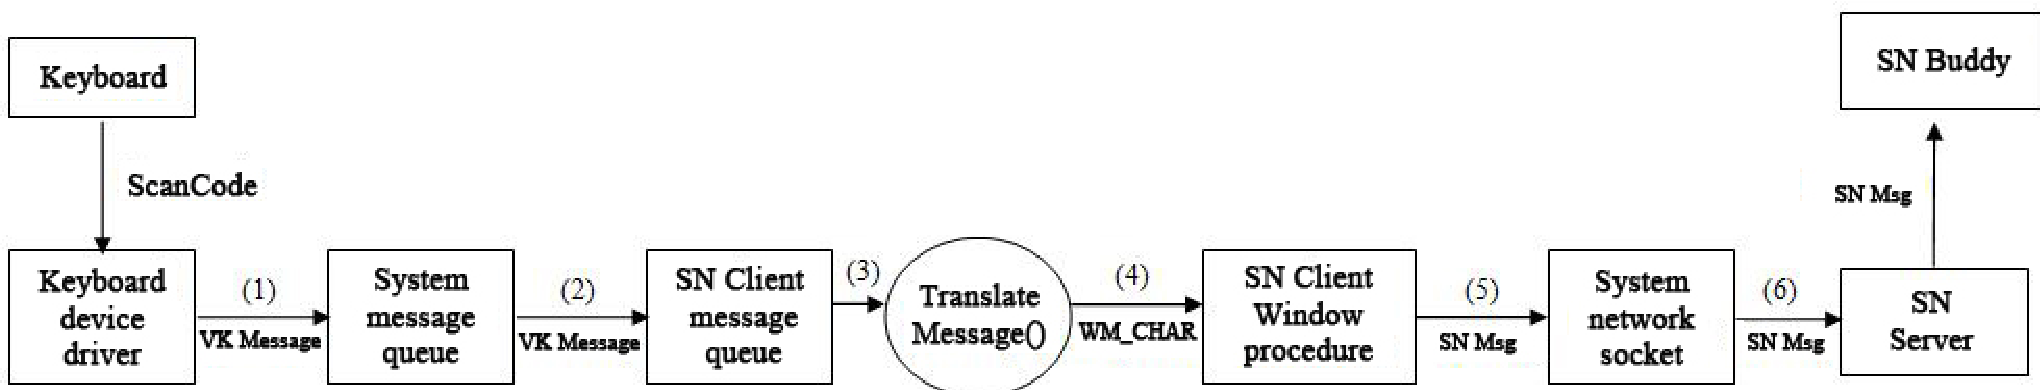
The genius of this approach is its use of Homograph Attacks. By replacing an ASCII 'o' with a Cyrillic 'о', the URL looks identical to the human eye but directs the browser to a malicious server.
Experiments: Why This Is Highly Effective
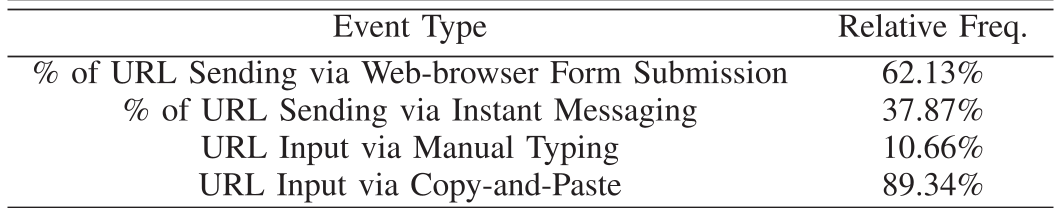
The study monitored 11 users to see how they handle URLs. The findings were stark:
- 90% of URLs were shared via Copy-and-Paste (making AV III particularly lethal).
- 100% Click-through Rate: Because the malicious link was embedded in a legitimate dialogue (e.g., "Check out this news! [Link]"), receivers did not hesitate to click.
| Attack Vector | Effort Level | Reach | Limitations |
|---|---|---|---|
| HTML Form | Application | Browser Only | Hard to inject code |
| Keystroke | OS Hook | System-wide | Depends on homograph support |
| Clipboard | OS Listener | System-wide | Very stealthy, no root needed |
| Network | Gateway | Network-wide | Fails with SSL/Encryption |
Critical Insights: Defending the "Hitch"
The paper concludes that purely behavioral or network-based defenses are insufficient. To counter Hitchbot, the industry needs:
- Sender-side Integrity: Implementing "Keystroke Encryption" or trusted paths to ensure that the text entered by a user is what the application actually receives.
- Receiver-side Lexical Analysis: Moving beyond blacklists to analyze the lexical structure of URLs (looking for homographs) in real-time.
Conclusion
Hitchbot proves that the strongest part of a security system—the human trust bond—can be converted into its weakest link. By piggybacking on legitimate behavior, attackers can bypass the "uncanny valley" of bot interactions. As social platforms become more central to our communication, the integrity of the local I/O chain becomes a front-line defense in cybersecurity.