
Integrating Technical and Legal Concepts of Privacy: Bridging Science and Policy
Integrating Technical and Legal Concepts of Privacy
This paper provides a comprehensive interdisciplinary survey of the legal and technical landscapes of privacy protection, with a focus on the EU General Data Protection Regulation (GDPR) and the mathematical framework of Differential Privacy. It argues for an integrated "Privacy-by-Design" approach to bridge the gap between ambiguous legal requirements and precise technical implementations.
TL;DR
In an era where "digital records of behavior" can predict your sexual orientation, religious views, and personality traits with unsettling accuracy, the concept of privacy has reached a breaking point. This paper, authored by Ana Sokolovska and Ljupco Kocarev, serves as a high-level blueprint for merging the General Data Protection Regulation (GDPR) legacy with the mathematical rigor of Differential Privacy. It aims to move from ambiguous legal prose to a "Privacy-by-Design" engineering reality.
Problem & Motivation: The End of Privacy as We Know It
The authors start with a chilling reality check: search rankings and Facebook "likes" are being weaponized to shift election outcomes and profile entire adult populations. Traditional privacy methods—simply removing your name from a spreadsheet—are useless against modern auxiliary information attacks.
The core friction lies in a "lost in translation" effect:
- Legal frameworks: Use terms like "meaningful overview" and "significantly affects," which are open to subjective judicial interpretation.
- Technical frameworks: Require precise definitions, yet often ignore the social and legal context of the data they protect.
Methodology: The Convergence of Law and Math
The paper advocates for a convergence centered on the concept of Privacy-by-Design. It breaks down the technical framework into two pillars:
1. Differential Privacy (The Gold Standard)
Unlike group anonymization (k-anonymity), which can be broken by cross-referencing datasets, ε-Differential Privacy provides a provable guarantee. It ensures that the output of an algorithm is essentially the same whether or not a specific individual’s data is included.
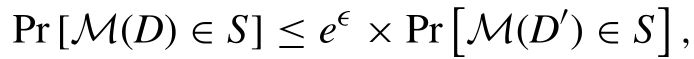 The mathematical soul of modern privacy: ensuring the probability of an outcome is bounded by the privacy loss parameter ε.
2. The Fairness Doctrine
Privacy is no longer just about hiding data; it’s about the fairness of the decisions made by that data. The authors highlight a crucial mathematical hurdle: the Incompatibility Theorem. You cannot simultaneously satisfy:
- Calibration within groups (predictive parity).
- Balance for the negative class (equal false negatives).
- Balance for the positive class (equal false positives).
Experiments & Results: The Fundamental Law of Information Recovery
The paper references a sobering principle known as the Fundamental Law of Information Recovery: Overly accurate estimates of too many statistics completely destroy privacy.
There is an inevitable trade-off curve between Data Utility (how useful the analysis is) and Privacy Loss (measured by ε). The authors note that major tech players like Google (PROCHLO system) and Apple (iOS 10) have already begun implementing these frameworks to balance this equation at scale.
 Architecture of privacy: Integrating social implications with technical guardrails.
Critical Insight: The Privacy Paradox
One of the paper’s most intriguing observations is the "Privacy Paradox": users often claim to value privacy while freely giving away personal data for minor conveniences.
The authors argue that technical solutions must account for this human behavior through:
- Personalized Privacy: Empowering users to control their own "privacy budget."
- Context-Aware Systems: Adapting privacy policies dynamically based on the sensitivity of the immediate environment.
Conclusion: A Proactive Future
The authors conclude that "privacy as we have known it has ended," but a new era of Accountable Algorithms is unfolding. The path forward is not just passing more laws, but encoding those laws into the very architecture of our software (Legal XML, Ontologies, and DP-native code).
Key Takeaway: For researchers and developers, privacy is no longer a "feature" to be added post-processing—it is a fundamental constraint of the system’s design, requiring a deep understanding of both the law and the limit of the ε-parameter.