
PEKING: Solving the Privacy Bottleneck in Distributed Social Networks
On key issuing privacy in distributed online social networks
This paper introduces PEKING, a Privacy Enhanced Key IssuiNG scheme for distributed Online Social Networks (OSNs) using Identity-Based Cryptography (IBC). It leverages Key Privacy Assistants (PAs) and a Byzantine Fault Tolerance (BFT) protocol to ensure secure private key distribution without requiring pre-existing secure channels.
TL;DR
Distributed Online Social Networks (OSNs) promise privacy by removing central authorities, but they struggle with secure key distribution. PEKING introduces a framework using Identity-Based Cryptography (IBC) that eliminates the need for secure channels and prevents the Key Generation Center (KGC) from spying on users. By enlisting a user's friends as Key Privacy Assistants (PAs), it achieves a decentralized trust model that is both fast and scalable to millions of users.
Problem & Motivation: The "Secure Channel" Paradox
In a centralized world, Facebook or X holds your data and your identity. Distributed OSNs try to fix this, but they face a cryptographic hurdle: How do you give a user their private key securely without an already secure connection?
Most Identity-Based Cryptography (IBC) systems assume a "Secure Channel" exists for key delivery. If you send a private key over an open network, it's vulnerable to:
- The Eavesdropper: Intercepting the key during transit.
- The Rogue Provider: The KGC itself can generate your key and read your messages (the Key Escrow problem).
- The Insider: Malicious nodes pretending to help while stealing data.
PEKING’s insight is simple but powerful: Trust your friends, not just the provider.
Methodology: Decentralized Key Issuing
PEKING splits the power of key generation between a central KGC and several distributed Privacy Assistants (PAs).
1. Peer Registration (Threshold Security)
When a user joins, the KGC doesn't send the ID and registration proof directly. Instead, it uses Shamir’s (k, n) Threshold Secret Sharing. The registration data is split into pieces and sent to different PAs. The user must collect at least pieces to reconstruct their ID. This prevents any single malicious PA from knowing who is joining.
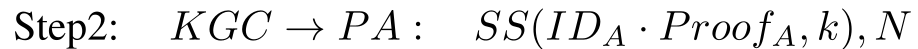
2. The 4-Step Key Issuing Framework
To get a final private key, the user interacts with both the KGC and the PAs:
- KGC Request: User requests a partial key.
- KGC Response: KGC provides a partial key (but cannot form the whole key).
- Blind PA Request: User requests the remaining secret components from their friends (PAs).
- Key Retrieval: The user combines these partial keys locally to form the master private key.
3. Cleaning the Network: BFT Authentication
How do we know the PAs (friends) are behaving? PEKING uses a Byzantine Fault Tolerance (BFT) scheme. The KGC sends anonymous "challenge" queries via relay nodes. If a PA fails to prove it holds the correct secret share, the BFT protocol identifies and removes them from the network.
Experiments & Results: Performance at Scale
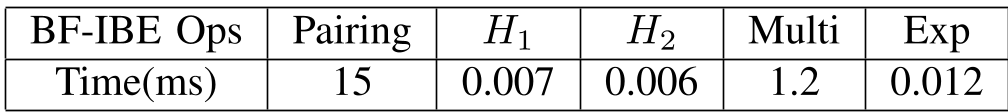
The authors implemented a prototype using the Boneh-Franklin IBE library.
Computational Efficiency
The overhead for adding this security layer is remarkably low:
- KGC Processing: ~19ms per request.
- PA Processing: ~21ms per request.
Scalability
The math shows that even with a modest CPU, a single KGC can handle 2.57 million users if they refresh their keys daily. This proves that decentralized security doesn't have to mean slow performance.
Critical Analysis & Conclusion
Takeaway
PEKING successfully bridges the gap between the convenience of IBC (using your email/name as a public key) and the security of decentralized networks. By using Threshold Cryptography, it effectively neutralizes the "God-mode" threat of a central KGC.
Limitations
- Friendship Dependency: The system assumes users have enough "honest" friends to act as PAs. In very small or new networks, this threshold might be hard to meet.
- ISP Eavesdropping: The paper acknowledges that if an ISP captures all shares at a single entry point, the threshold security could fail, though they argue this is rare in P2P environments.
Future Outlook
As decentralized web (Web3) and Fediverse platforms grow, protocols like PEKING provide a blueprint for "Key Management as a Social Service," where our social circles protect our digital identities.