
Snap's Defense: Using Auxiliary Graphs to Shield Social Privacy
Practical Privacy-Preserving Friend Recommendations on Social Networks
The paper introduces a practical framework for privacy-preserving friend recommendations on social networks, specifically targeting cold-start scenarios. By utilizing phone contact books as an auxiliary graph to anchor recommendations, the authors enhance resistance against brute-force social graph de-anonymization attacks while maintaining high recommendation utility.
TL;DR
Social network "Friend Recommendations" (the "People You May Know" feature) are a double-edged sword: they drive engagement but can inadvertently leak your entire social circle to attackers. Snap Inc. researchers propose a practical solution that uses your phone contact book not just for discovery, but as a "firewall." By restricting the candidate graph to users anchored in your contact list and applying a randomized pruning logic, they raised the bar for attackers while increasing friendship conversion by 12.7%.
The "Friendship Leak" Problem: When Brute-Force Meets Algorithms
In a cold-start situation—where a user is new—recommendation engines work overtime to find connections. However, this creates a vulnerability. An attacker can create a cluster of fake accounts, link them to a target user, and then observe the resulting recommendations. If the platform recommends a specific person back to the attacker, it confirms a pre-existing relationship between that person and the target.
Previous attempts to solve this via Differential Privacy (DP) often failed in production. Adding enough "noise" to hide relationships usually makes the recommendations so irrelevant (e.g., suggesting a stranger across the globe) that the feature becomes useless.
Methodology: The Contact Book as a Trust Anchor
The core insight of this paper is simple but powerful: An attacker can easily follow you on an app, but they can't easily get into your phone's address book.
The authors construct a "Candidate Graph" through a three-step process:
- Seed Selection: Identify users () who actually have the target user's number in their physical phone contacts.
- Neighbor Pruning: Expand the graph to include friends of , but only if those friends have at least existing connections within the seed group.
- Randomization: To prevent an attacker from reverse-engineering the threshold, the value of is randomized per user based on local graph sparsity.
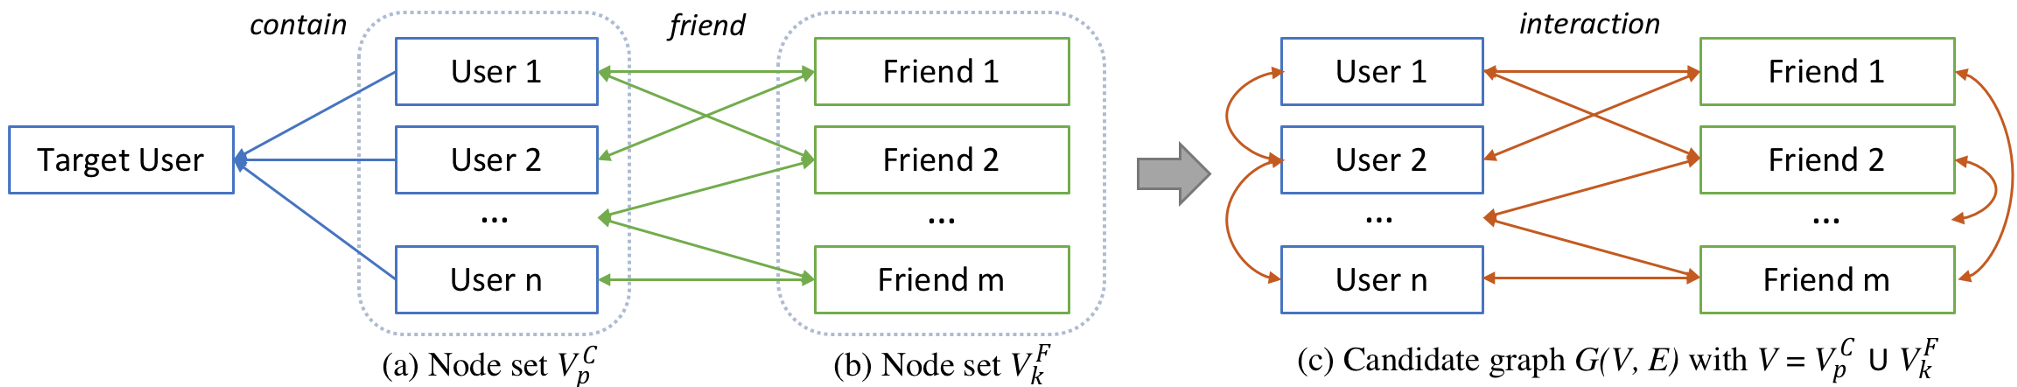 Figure 1: The workflow of building a privacy-preserving candidate graph. Note how the "Fk" set ensures that only well-connected, high-confidence neighbors are considered.
Experiments: Balancing Privacy and Utility
The researchers tested several graph variations (denoted as , , etc.) to see which provided the best balance of graph size (privacy) and User Engagement Score (UES).
| Metric | Phone Only () | Full Potential () | Pruned for Privacy () |
|---|---|---|---|
| **Nodes ( | V | )** | 36.8 |
| **Edges ( | E | )** | 37.3 |
| Engagement (UES) | 42.6 | 829.9 | 629.6 |
Note: Table data shows that pruning the graph () reduces the attack surface (fewer nodes/edges) while retaining over 75% of the engagement value of the full, un-pruned graph.
Critical Insight & Conclusion
Most academic privacy research focuses on perturbation (adding noise). This paper pivots to restriction (limiting the graph to a "trusted" subset). By utilizing an auxiliary graph (the contact book) that is significantly harder for an external adversary to manipulate, the system achieves "Privacy by Construction."
Takeaway for the Industry: In the age of AI-driven social engineering, relying on in-platform signals alone is a security risk. Integrating physical-world verification signals—like contact books or verified hardware IDs—into the recommendation pipeline is no longer just a UX choice; it's a privacy requirement.
Limitations: The method relies heavily on users opting into contact sharing. For users who do not share contacts, the cold-start recommendation remains either less private or less effective. Furthermore, the "PageRank-style" trust in contact books assumes that contact books themselves aren't compromised, which remains a vector for sophisticated targeted attacks.