
Unmasking the Social Web: How Active Attacks Exploit Network Topology
On analyzing and evaluating privacy measures for social networks under active attack
2018-09-17
Summary
Problem
Method
Results
Takeaways
Abstract
This paper investigates the "k-metric antidimension" as a privacy measure for social networks under active attacks, where an adversary injects nodes to re-identify others. The study combines theoretical proofs for tree topologies with extensive empirical evaluations across eight real-world social networks and multiple synthetic models (Erdös–Rényi and Barábasi–Albert).
## TL;DR
In an era of hyper-connectivity, your privacy isn't just about your name—it's about your "location" in the social web. This paper rigorously analyzes the **k-metric antidimension**, a measure of how easily an attacker can re-identify you by knowing your distance to a few controlled "seed" nodes. The verdict? Most real-world social networks are startlingly fragile, often requiring an attacker to control only a single node to break anonymity.
## The Structural Fingerprint
Prior research has shown that simply "de-identifying" a dataset is insufficient. In social networks, the topology itself is a fingerprint. If an attacker injects a few nodes—an **active attack**—and measures the shortest path distances from these nodes to a target, they can often uniquely identify that target.
The authors focus on the **k-metric antidimension**. If a network has a k-antidimension of $k$, it means that given an attacker controls a specific set of nodes, there are at least $k$ nodes that look identical to the attacker. Thus, the re-identification probability is $1/k$.
## Theoretical Breakthrough: The Case of Trees
One of the core contributions is **Theorem 1**. The authors prove that for any tree $T$ (a graph with no cycles), if it supports a high level of privacy (a large $k'$), it *necessarily* supports every level of privacy below it.
* **The Intuition**: In a tree, adding nodes to the attacker's control set $S$ forces the remaining nodes to form connected components. By carefully choosing which branches to "occupy," the attacker can systematically shrink the equivalence classes of indistinguishable nodes.
* **The Warning**: The paper notes that if a network is a tree, it is inherently easier to "partition" and thus potentially more vulnerable if not designed carefully.
## Methodology: Measuring Vulnerability
The authors applied two primary algorithms to find:
1. **$k_{opt}$**: The maximum level of "indistinguishability" a network can offer.
2. **$L_{opt}$**: The minimum number of nodes an attacker must control to reach a certain privacy threshold.

*Fig 1: Mathematical formulation of metric representation and equivalence classes.*
## Experimental Insights: Real vs. Synthetic
The researchers tested eight real networks, including the Zachary Karate Club and Enron email datasets.
### 1. Real-World Fragility
In almost all real networks (except Hamsterster friendships), an attacker controlling **just one node** could uniquely identify targets.
* **Enron Exception**: The Enron network showed high resilience, but for a strange reason—it would take an attacker controlling 86% of the nodes to successfully perform the attack, suggesting its structure is naturally "noisy" for this specific attack vector.
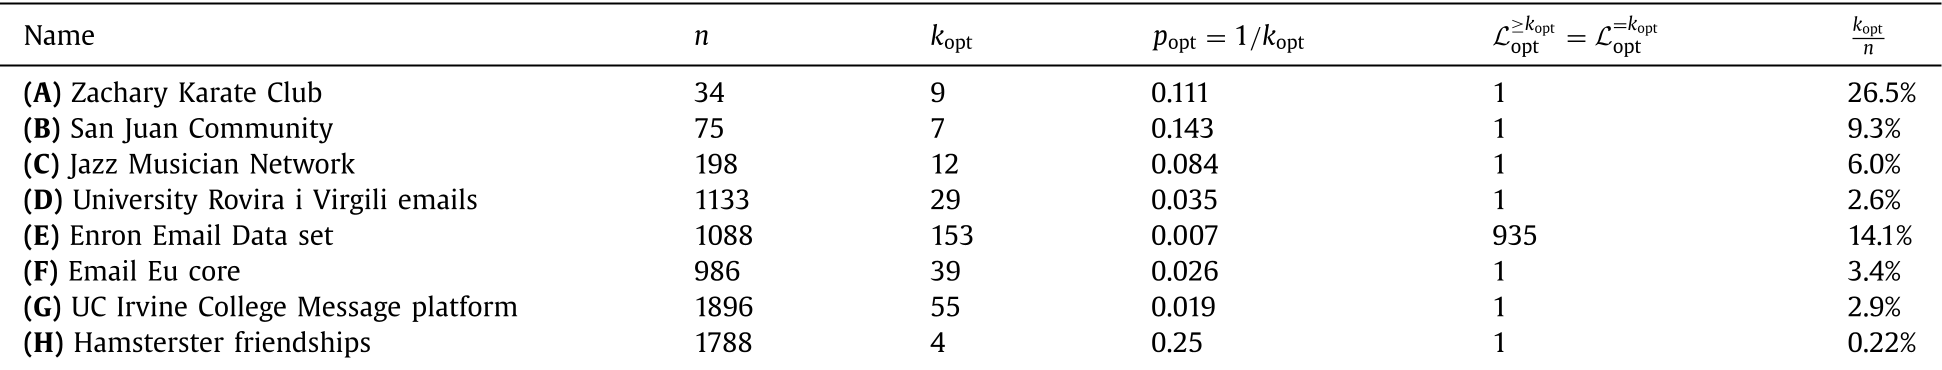
*Table 1: Optimal k and attacker requirements for real-world datasets.*
### 2. Scale-Free vs. Random
* **Erdös–Rényi (ER)**: Sparser random networks were more secure than dense ones.
* **Barábasi–Albert (BA)**: These "scale-free" networks (which mimic real social growth) were significantly more vulnerable than ER networks. The presence of "hubs" (highly connected nodes) likely gives attackers powerful vantage points to calculate distances.
## Critical Analysis & Takeaways
The study proves that **active attacks are a low-cost, high-reward strategy** for malicious entities. While $L_{opt}$ is a theoretical minimum, the empirical reality is that $L_{opt}=1$ in most social contexts.
**Limitations**: The study assumes the attacker has full knowledge of the network topology (the "Oracle" view). In practice, getting the full global graph is hard, though not impossible for sophisticated actors.
**Conclusion**: For product engineers, the takeaway is clear: structural anonymity is not a side effect of large numbers; it is a property of graph topology. If your network topology mimics a scale-free graph, you are likely highly vulnerable to distance-based re-identification.