
Decoupling Trust from Authority: A Public-Key Approach to Private Social Relationships
A Public-Key Protocol for Social Networks with Private Relationships
This paper proposes a public-key cryptographic protocol for social networks that secures "private relationships"—the specific types and trust levels between users. Unlike previous symmetric-key approaches, it enables decentralized access control and relationship verification without a central authority or trusted third party (TTP).
TL;DR
In the architecture of social networks, who you know is often as sensitive as what you post. While most privacy Research focuses on data encryption, this paper tackles path-privacy. It introduces a decentralized public-key protocol that allows users to prove they meet trust requirements (e.g., "Friend of a Friend" with 80% trust) without exposing the social graph to a central server or even the person requesting access.
The "Relationship Leak" Problem
Traditional Social Network Analysis (SNA) often assumes the graph is public or visible to a central provider (like Facebook). However, relationship metadata—the specific type (colleague, lover, creditor) and the trust level—is highly sensitive.
Prior SOTA efforts (notably by Carminati et al.) attempted to solve this using symmetric-key cryptography. However, these systems suffered from three fatal flaws:
- Centralized Dependency: They required a central node to store encrypted certificates and manage keys.
- Trusted Third Party (TTP): A central authority was needed to calculate transitive trust across paths.
- Revocation Complexity: Deleting a relationship required updating a global Certificate Revocation List (CRL).
Methodology: Public-Key Chains of Trust
The proposed protocol shifts the burden of proof from a central server to the nodes along the path.
The Core Mechanism
When User A wants to access a resource owned by User B, the protocol executes a multi-depth verification:
- Depth 1 (Direct): B checks their own records for A.
- Depth 2 (Indirect): If A and B aren't direct friends, A finds a mutual friend C. C sends a signed, encrypted certificate of their relationship with A directly to B using B’s Public Key.
- Mathematical Intuition: Instead of A carrying a "key" to B's data, the intermediaries (C, D, etc.) act as active verifiers. They compute the trust product (e.g., ) and pass the evidence forward.
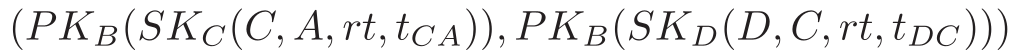 Figure 1: The mathematical representation of a Depth-3 certificate chain where A proves access through C and D to owner B.
Key Innovation: TTP-Free Revocation
The beauty of this protocol lies in its simplicity regarding "breakups." In a symmetric system, you must tell a server you no longer trust someone. In this public-key protocol, revocation is implicit. If C no longer trusts A, C simply refuses to send the certificate to B. No central list, no overhead.
Experiments & Comparative Analysis
The author validates the protocol by comparing its architectural overhead against the symmetric-key baseline across three dimensions:
| Feature | Symmetric-Key Baseline (Prior Work) | This Protocol (Public-Key) |
|---|---|---|
| Central Node | Required (Single Point of Failure) | Not Required (Fault Tolerant) |
| Trust Calculation | Done by Central TTP | Done by Resource Owner |
| Revocation | Heavy (CRL / Global Notification) | Lightweight (Local Refusal) |
| Privacy | Requestor sees encrypted certs | Requestor sees nothing |
Addressing "Type Leakage"
One subtle issue is that when an owner publishes an access rule (e.g., "Must be a Surgeon"), they leak their own affiliations. The paper suggests an ingenious (if slightly brute-force) solution: Camouflage. Owners publish many "bogus" relationship types alongside real ones, making it impossible for snoopers to discern the owner's true social circles.
Critical Insight & Conclusion
By moving to a public-key infrastructure, the paper successfully transitions social privacy from a storage problem (where do we keep keys?) to a routing problem (how do we find a willing path?).
Limitations:
- Incentives: Intermediate nodes must be "willing to collaborate." In a massive network, the computational cost of signing and encrypting for a stranger might require a micro-payment or reputation incentive not covered here.
- Public Key Infrastructure (PKI): The protocol assumes everyone has everyone else's public key, which remains a non-trivial challenge in purely peer-to-peer environments.
Future Outlook: This work lays the foundation for "Dark Social Networks" where the topology is entirely hidden, emerging only momentarily to facilitate a specific transaction or access request.