
Beyond Encryption: Why Your "Likes" Are Killing Your Privacy in Social Networks
Recipient Privacy in Online Social Networks (Short Paper)
This paper identifies critical vulnerabilities in recipient privacy within Online Social Networks (OSNs) and proposes a novel metric called "Frientropy" to quantify the anonymity of a recipient set. It introduces a new "Membership Query Security" definition to address privacy leaks caused by interactive user behaviors like likes and comments.
TL;DR
Even if you encrypt your messages, your social interactions (likes, comments, replies) act as a "metadata leak" that can reveal who you are talking to. This paper introduces Frientropy, a framework to measure how much anonymity remains in a group when some members are compromise, and argues that traditional cryptography is failing the dynamic nature of Online Social Networks (OSNs).
Academic Position: This is a foundational "short paper" that bridges the gap between static Cryptographic Broadcast Encryption and the dynamic, interactive reality of modern social graphs.
The "Interactive" Problem: The Death of Recipient Privacy
In classic cryptography, Recipient Privacy means an outsider shouldn't be able to tell who a message is intended for. This works fine for a static file system. However, OSNs are built on interaction.
Imagine you share an encrypted photo with 10 friends. If one friend "likes" the post, an adversary (or the OSN provider) now knows that friend is in the recipient set. If your friend groups are distinct (low entropy), identifying just one or two people can reveal the entire target group via the social graph. Consequently, the paper argues that encryption alone is a false sense of security in an interactive environment.
Methodology: Introducing Frientropy
The authors propose Frientropy (a portmanteau of Friend and Entropy) to quantify the randomness of a recipient pool.
1. Mathematical Intuition
Frientropy captures the amount of randomness a set of subsets offers even if some users disclose themselves. Instead of just looking at the set , we look at the probability distribution over the power set of all potential friend groups .
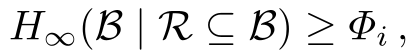
The formal definition uses Conditional Min-Entropy. If an adversary knows a subset of participants , the Frientropy is the log-probability of guessing the remaining set.
2. Threshold Sets and Social Graphs
Real social networks aren't random. Most people belong to specific clusters (family, work, hobby). The paper defines a Threshold : the minimum number of groups a person belongs to.
- Low Threshold: If you only belong to one social circle, revealing you as a recipient identifies that specific circle immediately.
- High Threshold: If you belong to many overlapping circles, the adversary remains uncertain about which group the message was intended for.
Membership Query Security: The New Adversary Model
The authors elevate the threat model by introducing Membership Query Security. Unlike traditional models where the adversary just watches the ciphertext, here the adversary can ask: "Is User X in the recipient set?" (mimicking a system admin checking logs or observing interaction).
The paper proves a direct link:
Theorem: The advantage of an adversary making queries is bounded by , where is the Frientropy.
Experiments & Results: The "Sanity Check"
While the paper is theoretical, it provides a "sanity check" calculation for complete sets versus threshold sets.
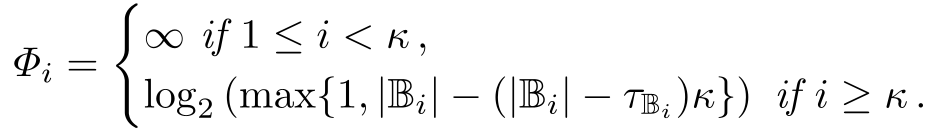
The result shows that frientropy decreases drastically as the set becomes more "incomplete" (i.e., more aligned with real-world social cliques). To counter this, the authors suggest Dummy Recipients—adding random users to the encrypted set who receive "garbage" keys. This artificially inflates the Frientropy, making it harder for an observer to distinguish the real target group.
Critical Insights & Takeaways
- Metadata is the Message: Secrecy of content is meaningless if the "who" is exposed. Encryption does not protect the social graph.
- Dummy Users are Necessary: In OSNs with 350+ average friends, social groups are highly predictable. Adding "noise" (dummy identities) is likely the only mathematical way to sustain privacy.
- Limitations: The paper acknowledges that dummy users don't interact. An advanced adversary could filter out dummies by observing that they never "like" or "comment" on the post, effectively reverting the Frientropy to its original low state.
Conclusion: Frientropy provides a vital metric for the next generation of privacy tools (like Scramble!). It shifts the focus from "how hard is the math?" to "how predictable is the social behavior?"