
SocACL: Strengthening OSN Privacy via Logic Programming and Attribute-Based Control
SocACL: An ASP-Based Access Control Language for Online Social Networks
SocACL is a formal Attribute-Based Access Control (ABAC) language designed for Online Social Networks (OSNs), implemented through a translation to Answer Set Programming (ASP). It enables fine-grained privacy management by utilizing user attributes, direct relationships, and complex relational chains as decision criteria.
TL;DR
SocACL (Social Access Control Language) is a high-level, formal access control language designed to solve the privacy "granularity gap" in Online Social Networks (OSNs). By bridging Attribute-Based Access Control (ABAC) with Answer Set Programming (ASP), it allows users to define highly specific rules based on who people are (attributes) and how they are connected (relationships), including complex logic like mutual friend counts.
Background: The Failure of Coarse-Grained Privacy
Social networks thrive on data disclosure, but this creates a massive attack surface for privacy breaches. Current systems often rely on binary "Friends/Public" toggles. Research shows that these settings frequently fail to reflect user intent because they ignore the context of the relationship or the specific attributes of the requester.
The authors argue that privacy in OSNs is essentially an access control problem. To solve it, we need a language that is as expressive as the social graph itself.
Methodology: The Power of Answer Set Programming (ASP)
The core innovation of SocACL is its formal foundation in Answer Set Programming (ASP). ASP is a declarative logic programming language optimized for difficult search and knowledge representation problems.
1. Unified Logic Foundation
SocACL translates high-level social policies into ASP rules. This allows the system to use inference engines (like DLV) to automatically determine if a user "Bob" should see "Alice's" profile based on pre-defined predicates.
2. Fine-Grained Syntax
Unlike traditional models, SocACL's EBNF (Extended Backus-Naur Form) supports:
- Attributes: Physical or digital traits (e.g.,
enrolled: 'UoL'). - Relationship Chains: Navigating the social graph through multiple "hops."
- Aggregates: Rules involving numbers, such as
count(e.g., "Must have at least 10 mutual friends").
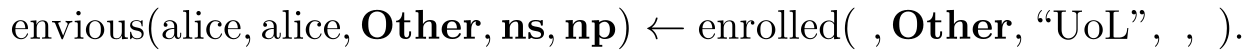 Figure 1: An example of an ASP translation where Alice defines a rule based on an 'enrolled' attribute.
Experiments & Comparisons: Beyond ReBAC
The paper compares SocACL to Relationship-Based Access Control (ReBAC). While ReBAC is good at handling hierarchical relationships (like "friend of a friend"), it lacks the ability to filter by attributes or perform mathematical operations on the graph.
| Feature | ReBAC | SocACL |
|---|---|---|
| Attribute Filtering | Limited | Native (ABAC integration) |
| Relational Chains | Composition-based | Hop-based (Explicit distance) |
| Aggregates (Sum/Min/Max) | No | Yes |
| Formal Logic Base | Varies | ASP (Formal Semantics) |
For instance, SocACL can handle a request like: "Allow access to coworkers who are also alumni of my university and share at least 3 common interests." This level of multi-dimensional filtering is the "Holy Grail" of OSN privacy.
Critical Insight & Conclusion
The true value of SocACL lies in its declarative nature. Users (or the systems representing them) don't need to program the how of the search; they simply define the what of the policy.
Limitations: While the logic is sound, the paper doesn't deeply explore the computational overhead of running an ASP solver every time a profile is viewed. In a network like Facebook with billions of nodes, the performance of the DLV engine would be a critical bottleneck.
Future Outlook: SocACL provides a blueprint for "Smart Privacy." As we move toward decentralized social media (like Mastodon or BlueSky), having a formal, portable language for access control will be essential for user-centric data sovereignty.