
To Share or Not to Share: Bridging the Privacy-Trust Gap in Mobile Social Networks
To Share or not to Share: Supporting the User Decision in Mobile Social Software Applications
This paper introduces the Mobile Access Control List (Macl), a conceptual privacy management framework for Mobile Social Software (MoSoSo). It formalizes a decision-making model based on the trade-off between privacy loss and trust gain to support selective data sharing among mobile users.
TL;DR
Mobile Social Software (MoSoSo) thrives on sharing, yet privacy remains its "Achilles' heel." This paper introduces a conceptual model that transforms privacy from a static barrier into a dynamic trade-off calculation. By introducing the Mobile Access Control List (Macl), the authors offer a way to automate sharing decisions based on social distance, communication history, and environmental context.
Background: The Social Cost of Connectivity
As mobile devices evolved from simple phones into multimedia hubs, the potential for social interaction—sharing photos, location, and status—exploded. However, the authors argue that the "cognitive load" of managing privacy manually for every interaction is unmanageable. If users find it too hard to manage, they simply won't share, stifling the growth of mobile social platforms.
The Core Intuition: Privacy as a Currency
The paper’s fundamental insight is that privacy isn't just about protection; it's about a utility maximization problem. Drawing on the "Trade-off between Privacy and Trust" theory, the authors propose that a user will (and should) only share data when:
Trust Gain > Minimal Privacy Damage
This shifts the focus from "how do we hide data?" to "how do we calculate the benefit of showing it?"
Methodology: The Macl Framework
To make this trade-off actionable, the authors propose a three-dimensional assessment focused on the User, the Recipient, and the Data.
1. Social Distance & Acquaintance
Instead of manually grouping contacts, the system utilizes communication logs (call frequency, SMS history) to infer social distance. Based on Moreno’s sociometry, it translates "network distance" into "social distance," assuming that higher interaction frequency implies higher trust.
2. The Mobile Access Control List (Macl)
The Macl is the engine of this framework. Unlike traditional firewall rules, it is tiered to optimize for user effort:
- Default Rules: Established via an initial survey to set general sensitivity (e.g., "Location is High Sensitivity").
- Contact Rules: Specific overrides for certain friends or family.
- Context Rules: Adapts sharing based on the environment (e.g., "At Work").
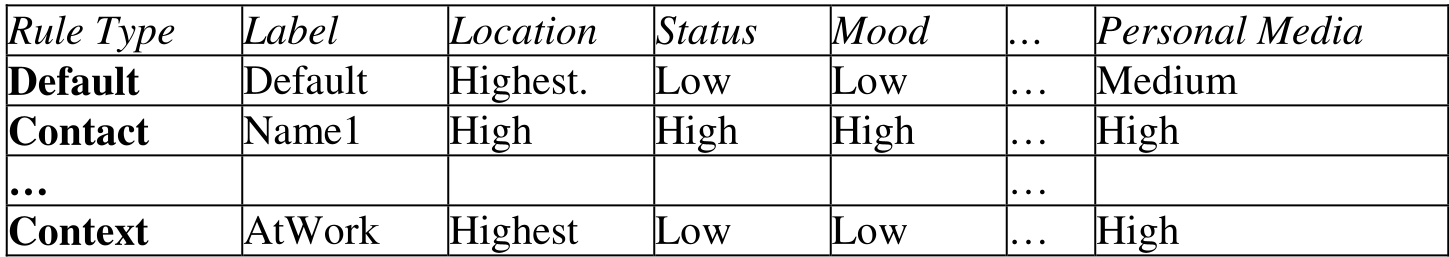 Table 1: The Macl structure demonstrating how rules override sensitivity based on context or identity.
Why It Works: Quantifying the Qualitative
The authors bridge the gap between human feeling (labels like "Medium Sensitivity") and machine logic (numerical weights). By assigning values (0 to 1) to these labels, the system can automatically compute whether a specific sharing request meets the user's "minimal damage" threshold.
Critical Insight & Future Outlook
While the paper provides a robust theoretical foundation, it acknowledges a classic HCI dilemma: The Reliability-Workload Trade-off. Manual rules are more accurate but exhausting, while automated rules are convenient but error-prone.
The authors suggest that future MoSoSo applications will need to function like "Spam Filters" for privacy—working silently in the background, only interrupting the user for high-stakes decisions. This early work laid the groundwork for modern "privacy assistants" found in today's mobile operating systems.
Conclusion
"To Share or Not to Share" remains a seminal question in the age of ubiquitous computing. This paper successfully frames the problem not as a security flaw, but as a social negotiation, suggesting that the future of privacy is not less sharing, but smarter sharing.