
TBPF-OSR: Redefining Privacy and Trust in Pervasive Computing Environments
A Novel Trust-Based Privacy Preservation Framework for Service Handling via Ontology Service Ranking
The paper introduces TBPF-OSR, a Trust-Based Privacy Preservation Framework utilizing Ontology Service Ranking and Fuzzy Logic to secure user authentication and service handling in pervasive computing environments. The system integrates an enhanced RSA variant for key generation and a dynamic trust evaluation mechanism, achieving superior performance in service recommendation and security robustness.
TL;DR
As pervasive computing integrates computing into daily life, traditional security models struggle with the dynamic nature of user roles and device heterogeneity. This paper introduces a Trust-Based Privacy Preservation Framework (TBPF-OSR) that combines an enhanced RSA algorithm, Ontology-based ranking, and Fuzzy Logic to ensure secure service handling. It yields higher trustworthiness (0.9823) and faster authentication than traditional methods.
Background & Motivation
In pervasive environments—like smart universities or healthcare systems—users access services from diverse devices (PDAs, Laptops, IoT nodes). Existing Access Control models like Context-RBAC are often too rigid. The core problem is Trustworthiness: How do we verify that a user should have access in a specific context (location, time, role) while ensuring the service they receive is reliable and private?
The authors' insight is that security shouldn't just be a "gatekeeper" (authentication) but also a "quality controller" (service ranking), ensuring that the data provided to the user is robust and the access is context-aware.
Methodology: The TBPF-OSR Engine
The framework operates through four critical phases:
1. Context-Aware Authentication
Instead of a simple password, the system uses an Enhanced RSA variant. It generates keys using normalized values from random primes, reducing the computational burden on mobile devices while maintaining high security.
2. Service Robustness Estimator
To prevent "malicious" or low-quality service handling, the system calculates a robustness score based on:
- Reputation: Tracking how often a service is accessed by current and other users.
- Sustainability: Predicting the "life time" of information based on the difference between the current year and the material's origin year.
- Ranking: A damping-factor-based algorithm similar to PageRank to evaluate a service's connectivity to other relevant resources.
3. Ontology Service Ranking & Fuzzy Recommendation
This is the "intelligence" layer. When a requested service is unavailable, an Ontology-based logic scans the user’s credentials (Department, Subject). A Fuzzy Logic Recommendation Algorithm then filters the available service list to provide the most relevant alternative, effectively acting as an automated librarian.
Experiments & Results
The authors conducted a rigorous comparison against existing standards like AES and SVD-based filtering.
- Key Generation Speed: The Enhanced RSA significantly outperformed standard AES, reducing latency from 12.87 ms to 7.24 ms, a critical gain for real-time pervasive systems.
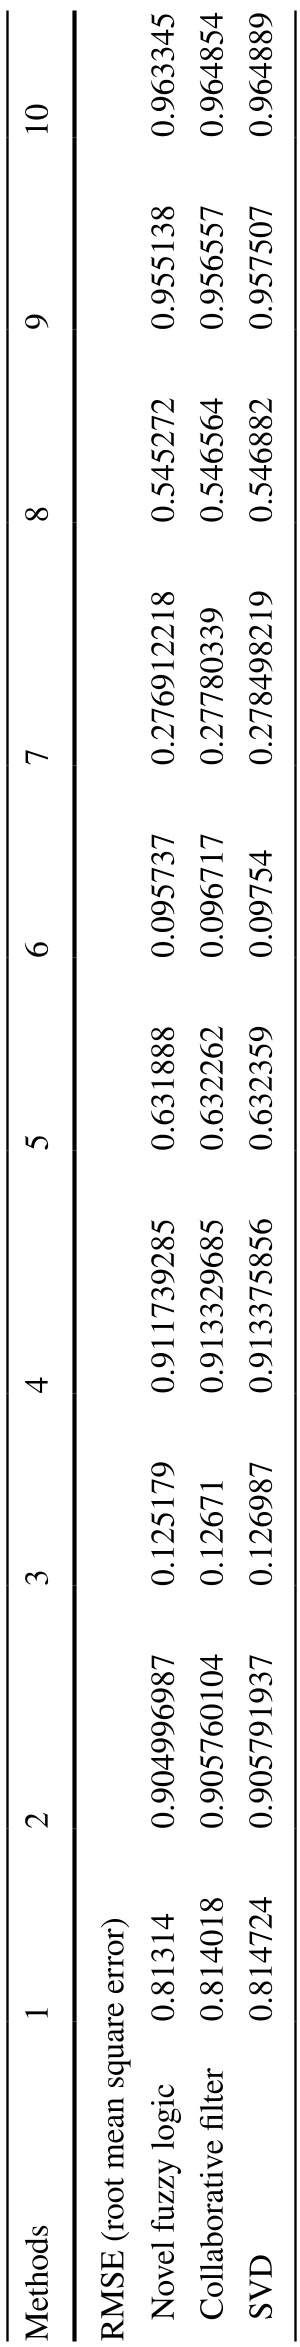
- Recommendation Accuracy: In terms of Mean Average Error (MAE) and Root Mean Square Error (RMSE), the Novel Fuzzy Logic approach consistently beat SVD and Collaborative Filtering across 10 different test iterations.
- Trust Convergence: The system showed that as interaction increases, the "Trustworthiness estimate" for positive users converges toward 0.98, while effectively flagging negative/malicious interactions.
Deep Insight & Conclusion
The TBPF-OSR framework success lies in its hybrid nature. It doesn't treat privacy as a static encryption problem but as a dynamic trust problem. By using Ontology Ranking, it bridges the gap between technical access control and semantic relevance.
Takeaways:
- Efficiency: The modified RSA demonstrates that we can achieve high security without the heavy overhead of standard cloud-based cryptosystems.
- Resilience: The fuzzy logic recommendation ensures that even when specific data is missing, the system provides safe, relevant alternatives instead of a "hard fail."
Limitations: While robust, the current model relies on a centralized "Role Manager." Future iterations could explore decentralizing this via Distributed Ledger Technology (DLT) to remove the single point of failure.
Academic References
- Zhou, L. et al. (2015). Trust enhanced cryptographic RBAC. IEEE Transactions on Information Forensics and Security.
- Rishwaraj, G. et al. (2016). Heuristics-based trust estimation. IEEE Transactions on Cybernetics.